Last updated: 10 November 2026
Docker shows up in almost every DevOps, cloud and backend interview. These 30 questions go from the basics to the topics senior engineers are tested on in 2026: multi-stage builds, BuildKit, image security with Docker Scout, and real debugging scenarios. Most answers include a short Dockerfile or command you can try.
Need a refresher first? Read What is Docker? and keep the Top 20 Docker commands open while you practise.
Docker Architecture in 2 Minutes
Many interviews open with "explain Docker's architecture". A clear answer covers five parts:
- Docker client (CLI): the
dockercommand you type. It sends requests to the daemon over a REST API, through a Unix socket or TCP. - Docker daemon (dockerd): the background service that builds images, manages networks and volumes, and asks containerd to run containers.
- containerd and runc: containerd manages container lifecycles and image pulls; runc creates the actual container using Linux namespaces (isolation of processes, network, mounts, users) and cgroups (limits on CPU, memory and I/O).
- Images and registries: images are stacks of read-only layers stored in registries such as Docker Hub or Amazon ECR.
- Docker objects: containers, images, networks and volumes, all managed through the same API.
Mentioning namespaces and cgroups by name shows you understand that containers are ordinary Linux processes with isolation, not tiny virtual machines.
How to Use This List
- Freshers (0–1 year): know Q1–Q15 well, with commands you can type from memory.
- 2–5 years: expect Q11–Q27, with "why" questions about layers, security and CI/CD.
- Senior and lead roles: expect the scenario questions, design trade-offs and production stories.
Answer every question in three steps: a one-line definition, how it works, and a real example from your work or a project.
Basic Docker Interview Questions
Q1. What is Docker?
Docker is a platform for building, shipping and running applications in containers. A container packages the app with its runtime, libraries and config, so it runs the same on a laptop, a CI runner and a production server.
Q2. What is the difference between a container and a virtual machine?
- Virtual machine: runs a full guest operating system on a hypervisor. Heavier, slower to start, strong isolation.
- Container: shares the host's kernel and isolates processes with namespaces and cgroups. Lightweight, starts in seconds, many per host.
In practice they work together: most cloud containers run inside VMs, which give strong isolation between customers, while containers give fast, dense packaging inside each VM. A good follow-up line: "Because containers share the kernel, a Linux container cannot run natively on a Windows kernel, which is why Docker Desktop uses a small Linux VM."
Q3. What is the difference between an image and a container?
An image is a read-only template made of layers. A container is a running (or stopped) instance of an image with a thin writable layer on top. One image can start many containers.
Q4. What is a Dockerfile?
A text file with instructions to build an image:
FROM node:22-alpine
WORKDIR /app
COPY package*.json ./
RUN npm ci --omit=dev
COPY . .
EXPOSE 3000
USER node
CMD ["node", "server.js"]
Q5. What are the most used Docker commands?
docker build -t myapp:1.0 .
docker run -d -p 8080:3000 --name web myapp:1.0
docker ps -a
docker logs -f web
docker exec -it web sh
docker stop web && docker rm web
docker images
docker pull nginx:1.27
docker push registry.example.com/myapp:1.0
Q6. What is Docker Hub and what is a registry?
A registry stores and serves images. Docker Hub is the default public registry. Teams also use Amazon ECR, Azure Container Registry, Google Artifact Registry, GitHub Container Registry or a self-hosted Harbor.
Q7. What is the difference between CMD and ENTRYPOINT?
ENTRYPOINT sets the main executable. CMD sets default arguments (or the default command if there is no ENTRYPOINT). Arguments passed to docker run replace CMD but not ENTRYPOINT.
ENTRYPOINT ["python", "app.py"]
CMD ["--port", "8000"]
Q8. What is the difference between COPY and ADD?
Both copy files into the image. ADD can also unpack local tar files and fetch URLs. Prefer COPY because it is predictable; use ADD only when you need its extra behaviour.
Q9. What are Docker volumes?
Volumes store data outside the container's writable layer, so it survives when the container is removed. Docker manages them under its own directory.
docker volume create pgdata
docker run -d -v pgdata:/var/lib/postgresql/data postgres:17
Q10. Volume vs bind mount vs tmpfs?
- Volume: managed by Docker, best for persistent app data.
- Bind mount: maps a host path into the container, handy for local development.
- tmpfs: stored in memory only, gone when the container stops.
Intermediate Docker Interview Questions
Q11. How do image layers and build caching work?
Each Dockerfile instruction creates a layer. Docker reuses a cached layer if the instruction and its inputs have not changed. Put rarely-changing steps (installing dependencies) before often-changing steps (copying source code) so rebuilds stay fast.
You can see an image's layers and their sizes with docker history myapp:1.0. Layers are shared between images that use the same base, so ten images built on python:3.12-slim store that base only once on disk and pull it only once. Deleting a file in a later layer does not shrink the image, because the file still exists in the earlier layer; clean up in the same RUN step that created the files.
Q12. What is a multi-stage build?
A Dockerfile with several FROM stages. You build in a large stage and copy only the output into a small final stage, so compilers and dev dependencies never reach production.
# build stage
FROM golang:1.23 AS build
WORKDIR /src
COPY . .
RUN CGO_ENABLED=0 go build -o /out/api ./cmd/api

# runtime stage
FROM gcr.io/distroless/static-debian12
COPY --from=build /out/api /api
USER nonroot
ENTRYPOINT ["/api"]
More ideas: How to reduce Docker image size.
Q13. What is BuildKit?
BuildKit is Docker's default build engine. It runs independent stages in parallel, caches better, and adds features such as cache mounts, build secrets and multi-platform builds through docker buildx.
# syntax=docker/dockerfile:1
RUN --mount=type=cache,target=/root/.cache/pip pip install -r requirements.txt
docker buildx build --platform linux/amd64,linux/arm64 -t myapp:1.0 --push .
Q14. What is Docker Compose?
Compose runs multi-container apps from one YAML file:
services:
  web:
    build: .
    ports:
      - "8080:3000"
    environment:
      DATABASE_URL: postgres://app:secret@db:5432/app
    depends_on:
      db:
        condition: service_healthy
  db:
    image: postgres:17
    environment:
      POSTGRES_USER: app
      POSTGRES_PASSWORD: secret
    volumes:
      - pgdata:/var/lib/postgresql/data
    healthcheck:
      test: ["CMD-SHELL", "pg_isready -U app"]
      interval: 5s
volumes:
  pgdata:
docker compose up -d starts it; docker compose down stops it. Full guide: Docker Compose tutorial.
Q15. What Docker network types exist?
- bridge: default; containers on the same user-defined bridge reach each other by name.
- host: container uses the host's network stack directly.
- none: no networking.
- overlay: spans several hosts (Docker Swarm).
- macvlan: gives a container its own MAC address on the physical network.
Q16. How do containers talk to each other?
Put them on the same user-defined network and use the container or service name as the hostname. Compose creates such a network automatically, which is why db:5432 works in the example above.
Q17. What is .dockerignore?
It lists files to leave out of the build context, such as .git, node_modules, logs and .env. It speeds up builds and stops secrets from being copied into images.
Q18. What is a HEALTHCHECK?
An instruction that tells Docker how to test whether the app inside is working:
HEALTHCHECK --interval=30s --timeout=3s CMD curl -f http://localhost:3000/health || exit 1
The container status then shows healthy or unhealthy.
Q19. How do you limit a container's CPU and memory?
docker run -d --memory=512m --cpus=1.5 myapp:1.0
If the container goes over the memory limit, the kernel kills it (exit code 137, OOMKilled).
Q20. What are restart policies?
--restart controls what happens when a container exits: no (default), on-failure[:N], always, or unless-stopped.
Advanced Docker Interview Questions
Q21. How do you secure Docker images?
- Start from small, trusted base images (Alpine, slim, distroless, Docker Hardened Images).
- Run as a non-root
USER. - Pin base image versions or digests.
- Never bake secrets into layers.
- Scan images in CI and fail on critical vulnerabilities.
- Sign images and generate an SBOM.
In an interview, add how you keep this up over time: a scheduled rebuild so base images pick up security patches even when the code does not change, and an agreed time to fix critical vulnerabilities (for example seven days).
Deep dive: Top 10 Docker best practices for production.
Q22. What is Docker Scout?
Docker Scout analyses an image's packages, lists known CVEs, suggests base image updates and can enforce policies. It works in Docker Desktop, Docker Hub and the CLI:
docker scout quickview myapp:1.0
docker scout cves myapp:1.0
docker scout recommendations myapp:1.0
Trivy and Grype are popular open-source alternatives.
Q23. How do you pass secrets safely?
At build time, use BuildKit secret mounts so the secret never lands in a layer:
RUN --mount=type=secret,id=npmrc,target=/root/.npmrc npm ci
docker build --secret id=npmrc,src=$HOME/.npmrc .
At run time, use Docker/Swarm secrets, Kubernetes Secrets or a vault, not plain ENV lines. See How to secure secrets in Docker containers.
Q24. How do you make images smaller?
Multi-stage builds, slim or distroless bases, combining RUN steps and cleaning package caches in the same step, a good .dockerignore, and installing only production dependencies.
Q25. What is the difference between Docker, containerd and runc?
Docker Engine is the full platform (CLI, API, builds, networking). It uses containerd to manage container lifecycles, and containerd uses runc to actually create containers using Linux kernel features. Kubernetes talks to containerd (or CRI-O) directly, without Docker Engine.
Q26. Docker Compose vs Docker Swarm vs Kubernetes?
- Compose: many containers on one host, mostly for development and small setups.
- Swarm: Docker's built-in clustering, simple but less used today. See What is Docker Swarm?
- Kubernetes: the standard for running containers at scale. See Docker vs Kubernetes.
Q27. How is Docker used in CI/CD?
The pipeline builds the image, tags it with the Git commit SHA, runs tests inside it, scans it, pushes it to a registry, and a deploy step (or a GitOps tool) rolls it out. Using the same image in every environment removes "works on my machine" problems.
A minimal GitHub Actions job:
- uses: docker/setup-buildx-action@v3
- uses: docker/login-action@v3
  with:
    registry: ghcr.io
    username: ${{ github.actor }}
    password: ${{ secrets.GITHUB_TOKEN }}
- uses: docker/build-push-action@v6
  with:
    push: true
    tags: ghcr.io/paperlive/api:${{ github.sha }}
    cache-from: type=gha
    cache-to: type=gha,mode=max
See How to build a CI/CD pipeline from scratch.
Scenario-Based Docker Interview Questions
Q28. A container exits immediately after starting. How do you debug it?
docker ps -ato see the exit code.docker logs <container>for the error.docker inspect <container>to check the command, env vars and mounts.- Run it interactively with a shell:
docker run -it --entrypoint sh myapp:1.0.
Common causes: the main process ends (a container lives only as long as PID 1), a missing env var, or a wrong CMD.
Q29. Your build is slow in CI. How do you speed it up?
Order layers for caching, use a .dockerignore, use BuildKit cache mounts, and share cache between CI runs with --cache-from / --cache-to (for example type=registry or type=gha on GitHub Actions). More tips: How to speed up slow CI/CD pipelines.
Q30. A container keeps getting killed with exit code 137. What does it mean?
137 means the process received SIGKILL, usually because it ran out of memory (check docker inspect for "OOMKilled": true). Raise the memory limit, fix the memory leak, or tune the runtime (for example, JVM heap settings) to stay within the limit.
Docker Networking Deep Dive
Networking questions trip up many candidates, so it is worth going one level deeper.
How port publishing works
-p 8080:3000 tells Docker to forward traffic from port 8080 on the host to port 3000 in the container. On Linux, Docker writes iptables (or nftables) rules to do this. That is why a published port can bypass a host firewall such as ufw unless you configure it carefully, a classic production surprise.
Default bridge vs user-defined bridge
On the default bridge network, containers can reach each other only by IP address. On a user-defined bridge (docker network create app-net), Docker runs an embedded DNS server, so containers find each other by name. Always use user-defined networks for multi-container apps.
Debugging network problems
docker network ls
docker network inspect app-net
docker exec -it web sh -c "nslookup db && nc -zv db 5432"
docker run --rm -it --network container:web nicolaka/netshoot
The last command starts a toolbox container that shares the web container's network namespace, so you can run curl, dig and tcpdump as if you were inside it, without installing tools in your app image.
Common networking answers
- A container cannot reach
localhoston the host, becauselocalhostinside a container is the container itself. Usehost.docker.internalon Docker Desktop or the host's IP on Linux. - Two containers on different user-defined networks cannot talk unless one is connected to both networks.
- Use
internal: trueon a Compose network to block outbound internet access for back-end services.
Docker on Kubernetes: What Changes
Most production containers now run on Kubernetes, so interviewers often ask how Docker skills translate.
- Images stay the same. Kubernetes runs any OCI image built with Docker, through containerd or CRI-O.
docker runflags become YAML. Ports becomecontainerPortand Services,-ebecomesenv,-vbecomes volumes and PersistentVolumeClaims,--memorybecomesresources.limits.- Restart policies and health checks change. Kubernetes uses liveness, readiness and startup probes instead of Docker
HEALTHCHECK, and controllers (Deployments) instead of--restart. See Kubernetes probes explained. - Secrets and config move to Kubernetes Secrets and ConfigMaps. See ConfigMaps vs Secrets.
- Compose files can be translated with tools such as Kompose, but most teams rewrite them as Helm charts or Kustomize overlays.
Start here: What is Kubernetes?
Docker Security Checklist
Use this checklist to answer any "how do you secure containers?" question:
- Minimal, pinned base image, rebuilt regularly to pick up patches.
- Multi-stage build so build tools never reach production.
- Non-root
USER, read-only root filesystem (--read-only) where possible. - Drop Linux capabilities (
--cap-drop ALL, then add back only what is needed) and never use--privilegedfor apps. - No secrets in the image, environment files or build args.
- Image scanning in CI (Docker Scout, Trivy) with a policy to fail on critical CVEs.
- Signed images and an SBOM for every release.
- Never mount the Docker socket (
/var/run/docker.sock) into an app container; it gives root on the host.
Read more in Secrets management in DevOps and Supply chain security and SBOMs.
Hands-On Exercise: Spot the Problems in This Dockerfile
Interviewers often show a Dockerfile and ask what is wrong. Try it before reading the answer:
FROM node:latest
COPY . /app
WORKDIR /app
RUN npm install
ENV DB_PASSWORD=SuperSecret123
EXPOSE 3000
CMD npm start
Problems and fixes:
node:latestis unpinned, so builds change without warning. Pin a version such asnode:22-alpine, or a digest.COPY . /appbeforenpm installbreaks layer caching: any code change reinstalls all dependencies. Copypackage*.jsonfirst, install, then copy the rest.npm installinstalls dev dependencies and ignores the lock file. Usenpm ci --omit=dev.- The password is baked into the image and visible with
docker history. Pass secrets at run time from a secret store. - No
.dockerignore, sonode_modules,.gitand.envmay be copied in. - The container runs as root. Add
USER node. - Shell-form
CMD npm startruns through/bin/sh, so signals such as SIGTERM may not reach Node and shutdowns are not graceful. Use the exec formCMD ["node", "server.js"]. - No
HEALTHCHECK.
Fixed version:
FROM node:22-alpine
WORKDIR /app
COPY package*.json ./
RUN npm ci --omit=dev
COPY . .
USER node
EXPOSE 3000
HEALTHCHECK --interval=30s --timeout=3s CMD wget -qO- http://localhost:3000/health || exit 1
CMD ["node", "server.js"]
Being able to list five or more of these problems is a strong signal in any Docker interview.
Rapid-Fire Docker Questions
Short answers for the quick-fire round many interviewers use.
- What does
docker ps -ashow? All containers, including stopped ones. - How do you see a container's IP address?
docker inspect -f '{{range .NetworkSettings.Networks}}{{.IPAddress}}{{end}}' web - What is a dangling image? An image layer with no tag, usually left after rebuilding. Remove with
docker image prune. - How do you free disk space?
docker system dfto see usage, thendocker system prune(add-a --volumescarefully). - Difference between
docker stopanddocker kill? Stop sends SIGTERM and waits (10 seconds by default) before SIGKILL; kill sends SIGKILL immediately. - What does
EXPOSEdo? It documents the port; it does not publish it. Publishing needs-pat run time. - What is the default network driver? bridge.
- Can a container have more than one process? Yes, but the convention is one main process per container; use Compose or Kubernetes to run several.
- What is
docker commit? It saves a container's changes as a new image. Avoid it for real builds because it is not reproducible; use a Dockerfile. - What is an image digest? A SHA-256 hash that identifies exact image content, for example
nginx@sha256:.... Tags can move; digests cannot. - What does
ARGdo vsENV?ARGis available only at build time;ENVis set in the image and visible at run time. - How do you copy a file out of a container?
docker cp web:/app/log.txt ./log.txt - What is Docker Desktop? A desktop app for Windows and macOS that runs the Docker Engine in a lightweight VM, with a GUI, Compose and an optional local Kubernetes cluster.
- What is
docker init? A command that generates a starter Dockerfile, Compose file and.dockerignorefor common languages. - What does
--rmdo? Removes the container automatically when it exits; handy for one-off commands.
Docker Commands Cheat Sheet for Interviews
# Images
docker build -t app:1.0 .
docker image ls
docker image history app:1.0
docker image rm app:1.0
docker tag app:1.0 registry.example.com/app:1.0
docker push registry.example.com/app:1.0

# Containers
docker run -d --name web -p 8080:3000 --restart unless-stopped app:1.0
docker ps -a
docker logs -f --tail 100 web
docker exec -it web sh
docker inspect web
docker stats
docker stop web && docker rm web

# Volumes and networks
docker volume ls
docker network create backend
docker run -d --network backend --name db postgres:17

# Compose
docker compose up -d --build
docker compose ps
docker compose logs -f web
docker compose down -v

# Clean-up
docker system df
docker system prune
The full explained list is in Top 20 Docker commands.
What Interviewers Expect at Each Level
Freshers
Clear definitions (image, container, Dockerfile, volume), the main commands, and one small project: for example a Python or Node app containerised and run with a database in Docker Compose. Honesty matters: say what you have done and what you have only read about.
2–5 years of experience
How you made images smaller and builds faster, how you handled secrets, how images move through your CI/CD pipeline, how you debugged a failing container, and how Docker images run on Kubernetes.
Senior engineers
Trade-offs and standards: base image policy, vulnerability management and SLAs for fixing CVEs, registry design, multi-architecture builds, supply-chain security (SBOMs, signing), and how you rolled these out across many teams.
Common Mistakes Candidates Make
- Calling containers "lightweight VMs" without explaining the shared kernel.
- Mixing up
CMDandENTRYPOINT, orCOPYandADD. - Saying "I would just use
latest" for production images. - Not knowing how to read logs or get a shell in a running container.
- Describing security only as "scan the image", without non-root users, minimal bases and secret handling.
- Giving textbook answers with no example from real work.
Sample Answer: "Tell Me About a Docker Project"
"Our Node.js API took 9 minutes to build in CI and the image was 1.2 GB. I rewrote the Dockerfile as a multi-stage build on node:22-alpine, copied only the production files into the final stage, added a .dockerignore, and turned on BuildKit cache mounts and registry caching in GitHub Actions. The image dropped to 160 MB, builds took under 3 minutes, and Docker Scout showed 80% fewer vulnerabilities because the smaller base had fewer packages. I also switched the container to a non-root user and moved secrets to AWS Secrets Manager."
Use the same shape for your own story: problem, what you changed, measurable result.
Docker Interview Tips
- Explain answers with a real project: "I containerised our Node API with a multi-stage build and cut the image from 1.1 GB to 180 MB."
- Know the commands well enough to type them without looking.
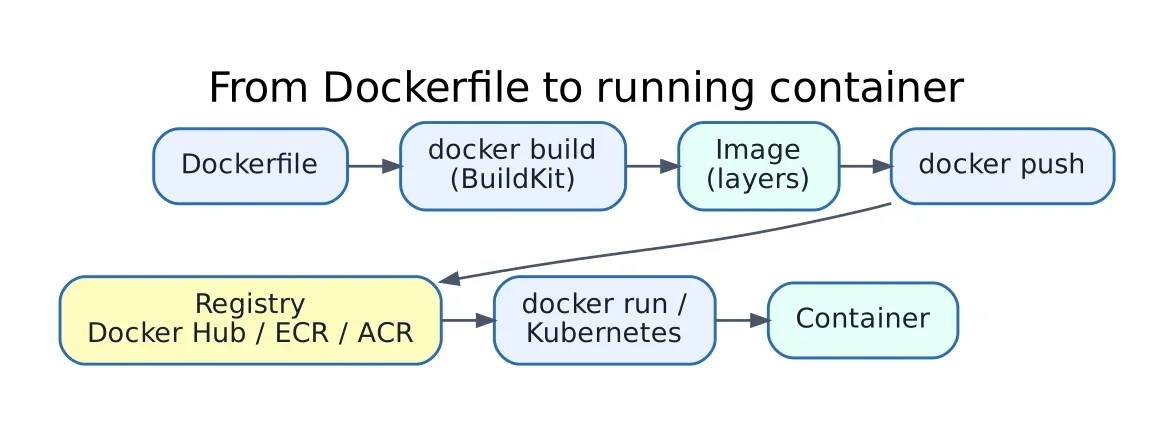
- Be ready to draw how an image goes from Dockerfile to registry to a running pod.
Learn Docker hands-on with real projects in our DevOps training. Next, try the Kubernetes interview questions and CI/CD interview questions.
Frequently Asked Questions
What Docker topics are asked most in interviews?
Images vs containers, Dockerfile instructions, layers and caching, volumes, networking, Docker Compose, multi-stage builds, image security and how Docker fits into CI/CD and Kubernetes.
Are Docker interview questions different for freshers and experienced engineers?
Yes. Freshers get definitions and basic commands. Experienced engineers get questions on image size, build speed, security scanning, debugging failed containers and running containers in production.
Do I need to know Kubernetes for a Docker interview?
For DevOps roles, yes at a basic level. Expect at least one question on how Docker images run on Kubernetes and how Docker Compose differs from Kubernetes.
How should I practise for a Docker interview?
Containerise a small app with a multi-stage Dockerfile, run it with a database using Docker Compose, scan the image with Docker Scout or Trivy, and push it to a registry from a CI pipeline.
What is the difference between Docker and Kubernetes?
Docker builds and runs containers on one machine. Kubernetes runs and manages containers across a cluster of machines, handling scheduling, scaling, self-healing and service discovery. Most teams use Docker (or a compatible tool) to build images and Kubernetes to run them in production.
How many Docker questions are asked in a DevOps interview?
Usually five to fifteen, depending on the role. Expect a few definitions, a Dockerfile or debugging exercise, and questions on how Docker fits into your CI/CD pipeline and Kubernetes setup.