Last updated: 10 November 2026
CI/CD questions come up in every DevOps interview, whatever tool the company uses. These 25 questions cover pipeline basics, deployment strategies, security (OIDC, SAST/DAST, supply chain), DORA metrics and real scenarios. Examples use GitHub Actions, with one Jenkinsfile for comparison.
Preparing for a Jenkins-heavy role? Use our dedicated Jenkins interview questions as well.
CI/CD Basics
1. What is CI/CD, and why does it matter?
Continuous Integration means developers merge small changes often and every change is built and tested automatically. Continuous Delivery/Deployment means every change that passes is ready to release, or is released automatically. Together they make releases small, frequent and low-risk. Read What is a CI/CD pipeline?
2. Continuous Delivery vs Continuous Deployment?
With continuous delivery, a person approves the release to production. With continuous deployment, every change that passes all checks goes to production automatically.

3. What are the key stages of a CI/CD pipeline?
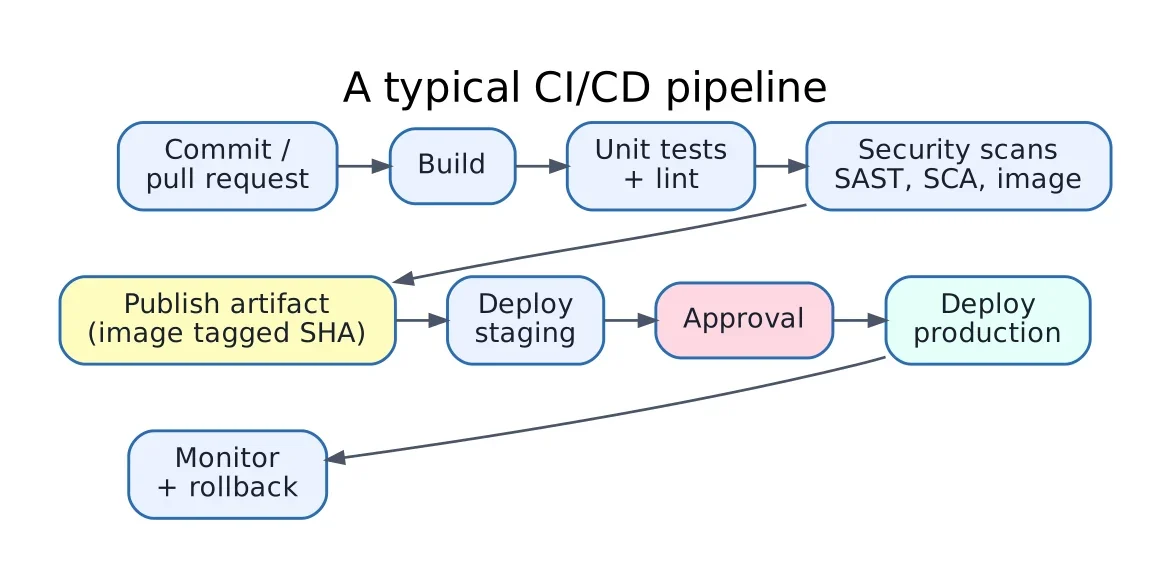
Source → build → unit tests → static analysis and security scans → package (image or artifact) → deploy to staging → integration/end-to-end tests → approval (if needed) → deploy to production → monitor.
4. What tools are commonly used?
- CI/CD servers: GitHub Actions, GitLab CI, Jenkins, Azure Pipelines, CircleCI.
- Build: Maven, Gradle, npm, Docker/BuildKit.
- Quality and security: SonarQube, Snyk, Trivy, CodeQL.
- Deploy: Helm, Argo CD, Flux, Terraform.
See Top 10 CI/CD tools.

5. What is a build artifact?
The output of a build that gets deployed: a JAR, a zip, a container image or a Helm chart. Build it once, store it in a registry with a unique version (often the commit SHA), and promote the same artifact through every environment.
6. What does "pipeline as code" mean? Show an example.
The pipeline is defined in a file in the repo, reviewed and versioned like code. A GitHub Actions workflow:
name: ci
on:
  pull_request:
  push:
    branches: [main]

jobs:
  test:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - uses: actions/setup-node@v4
        with:
          node-version: 22
          cache: npm
      - run: npm ci
      - run: npm test
The same idea in a Jenkinsfile:
pipeline {
  agent { docker { image 'node:22-alpine' } }
  stages {
    stage('Install') { steps { sh 'npm ci' } }
    stage('Test')    { steps { sh 'npm test' } }
  }
}
7. What are pipeline triggers?
Events that start a pipeline: push, pull request, tag, schedule (cron), manual run (workflow_dispatch), or another pipeline finishing.
Deployment Strategies
8. What is a blue-green deployment?
Two identical environments. Blue serves users while green gets the new version. After tests pass, traffic switches to green; blue stays ready for instant rollback. Guide: What is blue-green deployment?
9. What is a canary deployment?
The new version first gets a small share of traffic (for example 5%). If error rates and latency stay healthy, the share grows step by step to 100%. Compare both in Blue-green vs canary.
10. How do you roll back a failed deployment?
Redeploy the previous artifact version, switch traffic back (blue-green), roll back the release (helm rollback, kubectl rollout undo), or revert the commit in a GitOps repo. Database changes must be backward compatible so the old version still works. More: How to roll back safely.
11. What are feature flags and how do they help CI/CD?
Flags let you deploy code switched off and turn it on later for some or all users. Deployment and release become separate steps, so unfinished work can merge to main safely. See What are feature flags?
12. What is GitOps?
Git holds the desired state of the environment, and an agent in the cluster (Argo CD or Flux) pulls and applies it. CI builds and pushes the image; CD is a commit that updates the image tag. See What is GitOps?
Testing and Quality
13. Unit vs integration vs end-to-end tests?
- Unit: one function or class, fast, run on every commit.
- Integration: several components together (app + database).
- End-to-end: the full system through the UI or API, slowest, run before release.
Keep many unit tests and fewer end-to-end tests (the test pyramid).

14. How do you ensure code quality in a pipeline?
Linting, unit tests with a coverage threshold, static analysis with a quality gate (SonarQube), required code review, and branch protection that blocks merges when checks fail.
15. How do you speed up a slow pipeline?
Cache dependencies and Docker layers, run jobs in parallel, split tests across runners, only build what changed (path filters, monorepo tools), and use larger or self-hosted runners. Details: How to speed up slow CI/CD pipelines.
jobs:
  test:
    runs-on: ubuntu-latest
    strategy:
      matrix:
        shard: [1, 2, 3, 4]
    steps:
      - uses: actions/checkout@v4
      - run: npm ci
      - run: npx jest --shard=${{ matrix.shard }}/4
Security in CI/CD
16. How do you handle secrets in a pipeline?
Store them in the CI tool's secret store or a vault, scope them to environments, never print them, and prefer short-lived credentials over static keys. Scan commits for leaked secrets. See How to secure secrets in your CI/CD pipeline.
17. What is OIDC in CI/CD, and why is it better than access keys?
With OpenID Connect, the pipeline gets a short-lived signed token from the CI provider, and the cloud (AWS, Azure, GCP) exchanges it for temporary credentials. No long-lived cloud keys are stored anywhere.
permissions:
  id-token: write
  contents: read

steps:
  - uses: aws-actions/configure-aws-credentials@v4
    with:
      role-to-assume: arn:aws:iam::123456789012:role/github-deploy
      aws-region: ap-south-1
The IAM role's trust policy only allows tokens from your repo and branch.
18. What is SAST vs DAST, and where do they run in the pipeline?
- SAST (static) scans source code for flaws without running it. Run it on every pull request (CodeQL, Semgrep, SonarQube).
- DAST (dynamic) attacks the running app from outside. Run it against staging after deploy (OWASP ZAP).
- Add SCA for vulnerable dependencies and container/IaC scanning for images and Terraform.
Full comparison: SAST vs DAST.
19. What is software supply-chain security in CI/CD?
Making sure what you ship is what you built: pin actions and base images by version or digest, generate an SBOM, sign images (Sigstore cosign), produce build provenance (SLSA), and verify signatures before deploy. See SBOM explained.
Metrics and Culture
20. What are DORA metrics?
- Deployment frequency: how often you release to production.
- Lead time for changes: commit to running in production.
- Change failure rate: share of deployments that cause a failure.
- Time to restore service: how fast you recover from a failure.
Elite teams deploy on demand with lead times under a day. Read DevOps metrics that matter.
21. CI/CD vs DevOps: what is the difference?
DevOps is the culture and set of practices that join development and operations. CI/CD is one core practice inside it: the automated path from commit to production.
Scenario-Based CI/CD Questions
22. Tests pass locally but fail in CI. What do you check?
Different tool or dependency versions, missing environment variables or secrets, tests that depend on order, time zone or network, and files not committed to Git. Pin versions and run CI steps in the same container image you use locally.
23. Design a pipeline for a containerised microservice on Kubernetes.
name: release
on:
  push:
    branches: [main]
jobs:
  build:
    runs-on: ubuntu-latest
    permissions: { contents: read, id-token: write, packages: write }
    steps:
      - uses: actions/checkout@v4
      - run: npm ci && npm test
      - uses: docker/login-action@v3
        with:
          registry: ghcr.io
          username: ${{ github.actor }}
          password: ${{ secrets.GITHUB_TOKEN }}
      - uses: docker/build-push-action@v6
        with:
          push: true
          tags: ghcr.io/paperlive/api:${{ github.sha }}
  deploy-staging:
    needs: build
    runs-on: ubuntu-latest
    environment: staging
    steps:
      - run: echo "update image tag in GitOps repo to ${{ github.sha }}"
  deploy-prod:
    needs: deploy-staging
    runs-on: ubuntu-latest
    environment: production   # requires reviewer approval
    steps:
      - run: echo "promote ${{ github.sha }} to production"
Explain each choice: tests before build, image tagged with the commit SHA, OIDC/short-lived tokens, the same image promoted, and a protected production environment.
24. A bad release reached production. Walk me through your response.
Roll back first (previous image or traffic switch), confirm metrics recover, communicate status, then find the root cause in a blameless postmortem and add a test or check so it cannot happen again. See Incident management and blameless postmortems.
25. What challenges have you faced with CI/CD, and how did you fix them?
Pick one real example: flaky tests (quarantined and fixed them, added retries only for known flaky infra), slow pipelines (caching and parallel jobs cut 25 minutes to 8), or risky database changes (expand-and-contract migrations). Give numbers.
How to Prepare for CI/CD Interview Questions
- Build one pipeline end to end on GitHub Actions: test, build an image, scan it, deploy to a staging environment with OIDC, and promote to production with approval.
- Be able to draw the pipeline and explain each stage.
- Learn the vocabulary: artifacts, environments, gates, canary, DORA, SBOM.
Our DevOps training includes hands-on CI/CD projects. Also read How to build a CI/CD pipeline from scratch and CI/CD pipeline best practices.
Frequently Asked Questions
What are the stages of a CI/CD pipeline?
Source, build, test, security scan, package and publish an artifact, deploy to staging, verify, and deploy to production, with monitoring and rollback after release.
What are DORA metrics?
Four delivery metrics from the DevOps Research and Assessment team: deployment frequency, lead time for changes, change failure rate and time to restore service.
Which CI/CD tool should I learn for interviews?
Learn GitHub Actions or GitLab CI for modern teams and Jenkins for enterprises. The concepts (stages, artifacts, secrets, environments, approvals) are the same across tools.
How do I explain a CI/CD project in an interview?
Describe the problem, the pipeline you built (tools, stages, deployment strategy, security checks) and a measurable result such as faster deploys or fewer failed releases.