Last updated: 10 November 2026
These 20 AWS DevOps interview questions cover the areas interviewers test most: CI/CD with the AWS Code services, Infrastructure as Code, monitoring, security and architecture. Answers include real buildspec.yml, appspec.yml and CloudFormation snippets, and there is a section on the AWS DevOps Engineer Professional exam at the end.
Background reading: What is AWS DevOps?
1. AWS DevOps Interview Questions: Core Fundamentals
Q1. What is DevOps, and how does AWS support it?
DevOps is a way of working where development and operations share ownership, automate delivery and release small changes often. AWS supports it with managed CI/CD (CodePipeline, CodeBuild, CodeDeploy), Infrastructure as Code (CloudFormation, CDK), containers and serverless (ECS, EKS, Lambda) and monitoring (CloudWatch, X-Ray).
Q2. What's the difference between Continuous Integration, Delivery and Deployment?
CI builds and tests every change merged to the main branch. Continuous delivery keeps every passing build ready to release, with a manual approval for production. Continuous deployment releases every passing build automatically.
Q3. Explain the shared responsibility model in AWS.
AWS secures the cloud itself: data centres, hardware, networking and the managed service software. You secure what you put in the cloud: IAM, data, OS patches on EC2, security groups, encryption settings and application code. The split moves toward AWS as you use more managed services.
2. AWS DevOps Interview Questions on CI/CD Pipelines
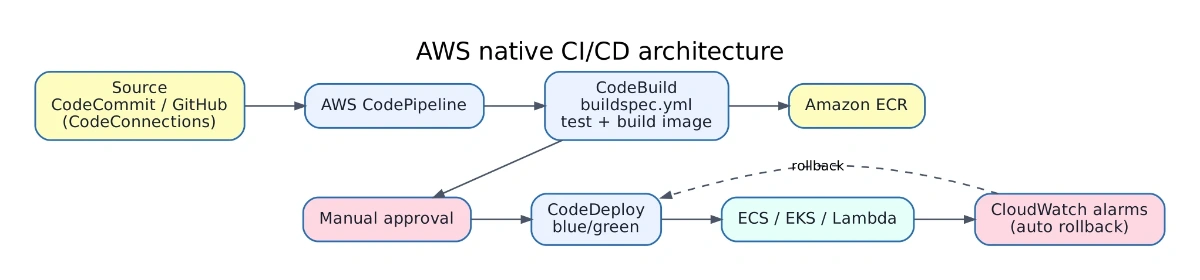
Q4. How would you design a CI/CD pipeline using AWS native services?
- Source: CodeCommit, GitHub or Bitbucket (through a CodeConnections connection).
- Build and test: CodeBuild runs
buildspec.yml, builds an image and pushes it to ECR. - Deploy: CodeDeploy (EC2, ECS blue/green, Lambda) or a CloudFormation deploy action.
- Orchestrate: CodePipeline with a manual approval before production.
- Observe: CloudWatch alarms that can stop or roll back a deployment.
A typical buildspec.yml:
version: 0.2
env:
  variables:
    REPO: 123456789012.dkr.ecr.ap-south-1.amazonaws.com/shop-api
phases:
  install:
    runtime-versions:
      nodejs: 22
  pre_build:
    commands:
      - aws ecr get-login-password | docker login --username AWS --password-stdin $REPO
      - TAG=${CODEBUILD_RESOLVED_SOURCE_VERSION:0:7}
  build:
    commands:
      - npm ci && npm test
      - docker build -t $REPO:$TAG .
  post_build:
    commands:
      - docker push $REPO:$TAG
      - printf '[{"name":"api","imageUri":"%s"}]' $REPO:$TAG > imagedefinitions.json
reports:
  unit-tests:
    files: ['junit.xml']
artifacts:
  files: [imagedefinitions.json]
cache:
  paths: ['/root/.npm/**/*']
Q5. What is AWS CodeCommit, and is it still available?
CodeCommit is AWS's managed private Git service. In July 2024 AWS stopped accepting new customers and suggested moving to GitHub, GitLab or Bitbucket. On 24 November 2025 AWS reversed this: CodeCommit returned to full general availability and is open to new customers again, with Git LFS support on its roadmap. In an interview, mentioning both events shows you follow AWS news. Many teams still use GitHub as the source and connect it to CodePipeline through CodeConnections.
Q6. What is a blue/green deployment on AWS, and when would you use it?
You run the new version (green) next to the current one (blue) and switch traffic once green is healthy. On AWS you can do this with CodeDeploy for ECS (two target groups behind an ALB), Elastic Beanstalk environment swaps, or weighted Route 53 records. Use it when you need near-zero downtime and instant rollback.
Q7. What deployment strategies does AWS CodeDeploy support?
- EC2/on-premises: in-place (AllAtOnce, HalfAtATime, OneAtATime) or blue/green.
- ECS: blue/green with canary or linear traffic shifting.
- Lambda: canary (for example 10% for 5 minutes) or linear (10% every minute) using aliases.
An appspec.yml for ECS:
version: 0.0
Resources:
  - TargetService:
      Type: AWS::ECS::Service
      Properties:
        TaskDefinition: <TASK_DEFINITION>
        LoadBalancerInfo:
          ContainerName: api
          ContainerPort: 8080
Hooks:
  - AfterAllowTestTraffic: "arn:aws:lambda:ap-south-1:123456789012:function:smoke-test"
3. AWS DevOps Interview Questions on Infrastructure as Code
Q8. CloudFormation vs Terraform: which one and why?
CloudFormation is AWS-native, free, keeps state for you and supports new AWS features quickly. Terraform works across clouds and SaaS tools, has a huge module ecosystem and a plan step many teams prefer. Choose CloudFormation/CDK for AWS-only shops that want no state to manage; choose Terraform for multi-cloud or existing Terraform skills. See Terraform vs CloudFormation.
Q9. What is a CloudFormation stack, and how do you handle changes safely?
A stack is a set of resources managed as one unit from a template. Use change sets to preview changes, stack policies to protect critical resources, termination protection, and drift detection to find manual changes.
AWSTemplateFormatVersion: '2010-09-09'
Parameters:
  Env:
    Type: String
    AllowedValues: [dev, prod]
Resources:
  LogsBucket:
    Type: AWS::S3::Bucket
    DeletionPolicy: Retain
    Properties:
      BucketName: !Sub 'paperlive-logs-${Env}'
      VersioningConfiguration:
        Status: Enabled
      BucketEncryption:
        ServerSideEncryptionConfiguration:
          - ServerSideEncryptionByDefault:
              SSEAlgorithm: aws:kms
Outputs:
  BucketArn:
    Value: !GetAtt LogsBucket.Arn
aws cloudformation create-change-set --stack-name logs-prod \
  --template-body file://logs.yaml --parameters ParameterKey=Env,ParameterValue=prod \
  --change-set-name v2
aws cloudformation describe-change-set --stack-name logs-prod --change-set-name v2
Q10. What are AWS CDK and SAM?
CDK lets you define infrastructure in TypeScript, Python, Java, C# or Go and synthesises CloudFormation templates. SAM is a CloudFormation extension with short syntax for serverless apps, plus a CLI to build, test locally and deploy Lambda functions.
4. AWS DevOps Interview Questions on Monitoring and Logging
Q11. How would you set up centralised logging for a multi-account setup?
Send CloudWatch Logs from each account to a central logging account using subscription filters or cross-account observability, store long-term copies in S3, and query them with CloudWatch Logs Insights or OpenSearch. Turn on an organization-wide CloudTrail trail to the same account.
Q12. What's the difference between CloudWatch Metrics, Logs and Alarms?
Metrics are numeric time series (CPUUtilization). Logs are text events from apps and services. Alarms watch a metric and act when it crosses a threshold: notify through SNS, scale with Auto Scaling, or roll back a CodeDeploy deployment.
aws cloudwatch put-metric-alarm --alarm-name api-5xx-high \
  --namespace AWS/ApplicationELB --metric-name HTTPCode_Target_5XX_Count \
  --dimensions Name=LoadBalancer,Value=app/shop-alb/abc123 \
  --statistic Sum --period 60 --evaluation-periods 3 --threshold 20 \
  --comparison-operator GreaterThanThreshold \
  --alarm-actions arn:aws:sns:ap-south-1:123456789012:oncall
Q13. What is AWS X-Ray?
A distributed tracing service. It follows a request across API Gateway, Lambda, ECS and databases and shows a service map with latency and errors at each hop. Many teams now send traces through the AWS Distro for OpenTelemetry.
5. AWS DevOps Interview Questions on Security
Q14. How do you manage secrets in an AWS DevOps pipeline?
Store them in Secrets Manager (with rotation) or SSM Parameter Store SecureString, give CodeBuild an IAM role that can read only what it needs, and reference them in the buildspec instead of hard-coding:
env:
  secrets-manager:
    DB_PASSWORD: prod/shop/db:password
  parameter-store:
    API_URL: /shop/prod/api_url
For GitHub Actions, use OIDC to assume an IAM role instead of storing access keys.
Q15. What is the principle of least privilege, and how do you apply it?
Give each user, role and pipeline only the permissions it needs. Use separate roles per pipeline stage, IAM Access Analyzer to generate policies from real activity, permission boundaries, and Service Control Policies in AWS Organizations to block risky actions account-wide.
Q16. How would you integrate security scanning into a CI/CD pipeline?
SAST and dependency scanning in CodeBuild on every pull request, Amazon Inspector scanning for ECR images, IaC scanning (cfn-lint, cfn-nag, Checkov) before deploy, and a failed build when critical findings appear. Guardrails after deploy: Security Hub, GuardDuty and AWS Config rules. Read CI/CD pipeline security.
6. Advanced AWS DevOps Engineer Interview Questions
Q17. How would you design a highly available, multi-region application?
Run the app in at least two AZs per region behind an ALB with Auto Scaling, replicate data across regions (Aurora Global Database, DynamoDB global tables, S3 replication), route users with Route 53 latency or failover records, deploy both regions from the same pipeline, and test failover regularly.
Q18. What's the difference between ECS and EKS?
ECS is AWS's own simpler container orchestrator, deeply integrated with AWS. EKS is managed Kubernetes, portable and with a large ecosystem, but more to learn and operate. Both can run on EC2 or Fargate. See Kubernetes vs ECS.
Q19. What is GitOps, and how does it work with AWS?
Git holds the desired state of your clusters. CI builds and pushes images to ECR; Argo CD or Flux running in EKS watches the Git repo and applies changes. Rollback is a Git revert. See What is GitOps?
Q20. Walk me through handling a production incident on AWS.
Acknowledge the alarm, check dashboards and recent deployments, roll back if a release caused it (CodeDeploy automatic rollback on alarm, or redeploy the last image), use Systems Manager for safe access instead of SSH, communicate status, and write a blameless postmortem with follow-up actions. See Incident management and blameless postmortems.
7. AWS DevOps Engineer Professional (DOP-C02) Exam
Exam facts
- Code: DOP-C02
- Format: 75 multiple-choice and multiple-response questions
- Time: 180 minutes
- Cost: USD 300
- Passing score: 750 out of 1000
- Valid for: 3 years
Always check the official AWS exam page before booking, as details can change.
Exam domains
- SDLC Automation: 22%
- Configuration Management and IaC: 17%
- Resilient Cloud Solutions: 15%
- Monitoring and Logging: 15%
- Incident and Event Response: 14%
- Security and Compliance: 17%
How to prepare
- Build a full CodePipeline with CodeBuild, CodeDeploy blue/green to ECS, and CloudWatch alarm rollback.
- Practise CloudFormation StackSets, change sets and drift detection across accounts.
- Learn Systems Manager (Automation, Patch Manager, Parameter Store), EventBridge rules and Organizations SCPs.
- Take timed practice exams; the questions are long, so time management matters.
8. Final Thoughts
Strong AWS DevOps candidates explain trade-offs, not just service names. Build one pipeline end to end, break it, and be ready to explain how you fixed it. For guided AWS DevOps labs, see our DevOps training. Also read Top 25 CI/CD interview questions and Terraform interview questions.
Frequently Asked Questions
Is AWS CodeCommit still available?
Yes. AWS stopped new sign-ups in July 2024, but on 24 November 2025 it returned CodeCommit to full general availability and reopened it to new customers.
What AWS services should a DevOps engineer know?
IAM, EC2, VPC, S3, CodePipeline, CodeBuild, CodeDeploy, CloudFormation or CDK, ECS and EKS, Lambda, CloudWatch, X-Ray, Systems Manager and Secrets Manager.
Is the AWS DevOps Engineer Professional exam hard?
Yes, it is a professional-level exam with long scenario questions. Most candidates have two or more years of hands-on AWS experience and often hold an associate certification first.
Do AWS DevOps interviews ask about Terraform?
Often, yes. Many AWS teams use Terraform instead of or alongside CloudFormation, so be ready to compare them and explain remote state.